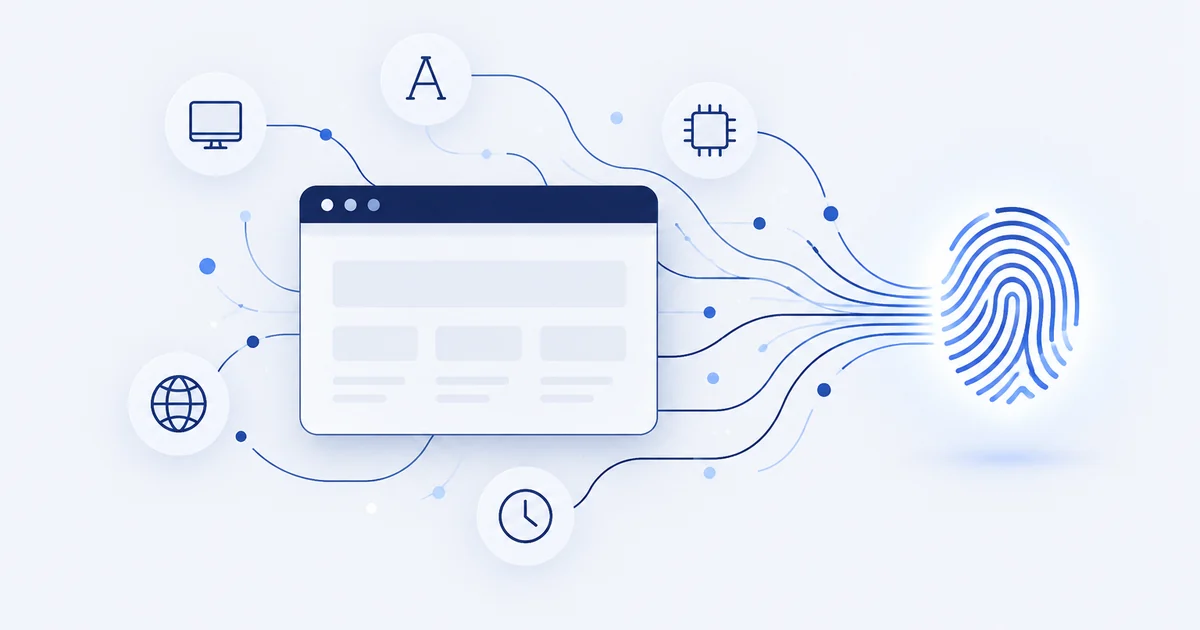
Browser fingerprinting is a way for a website to recognise your device by combining many small details your browser shares, such as screen size, fonts, graphics hardware, language and time zone, without storing anything on your computer. Because the combination is often unique, it can identify you even after you clear cookies or use private browsing.
How is a fingerprint different from a cookie?
A cookie is a small file a site saves in your browser. You can see it, and you can delete it.
A fingerprint is not stored on your device. The site reads information your browser already gives away, runs it through a calculation, and gets a short identifier. If the same identifier shows up on your next visit, the site recognises you, even with no cookie present.
| Cookie | Fingerprint | |
|---|---|---|
| Stored on your device | Yes | No |
| You can delete it | Yes | No |
| Survives “clear cookies” | No | Yes |
| Survives private browsing | Usually not | Often yes |
What can websites see about your browser?
Every site you visit can read a long list of values. The main groups are:
- Browser and system: browser name and version, operating system, language, time zone.
- Screen: resolution, colour depth, pixel ratio, available window size.
- Hardware hints: number of CPU cores, device memory, touch support.
- Fonts: which fonts are installed, which differs between computers.
- Graphics (WebGL): the graphics card and driver, as reported to the browser.
- Canvas and audio: how your device draws a hidden image or processes a short sound. Tiny hardware and software differences produce slightly different results.
- Network: your IP address, and in some cases addresses revealed through WebRTC.
No single value identifies you. The combination does.
Why can a fingerprint be unique?
Each value on its own is shared by many people. Millions of people use the same browser version. But as values stack up, fewer and fewer people match all of them. This is the same reason a short list of facts about a person (age, town, job, car) can point to one individual.
The best-known early study came from the Electronic Frontier Foundation. In 2010 it collected fingerprints from 470,161 browsers. Among those visitors, who were mostly privacy-conscious people, 83.6% of browsers had a fingerprint that no other browser in the sample shared (Peter Eckersley, “How Unique Is Your Web Browser?”, 2010). The same study found that the figure rose to 94.2% for browsers with Flash or Java enabled. Both plugins are now largely obsolete, and browsers have changed since, so treat these numbers as a demonstration of the principle and not as today’s rate. The principle still holds.
Who uses fingerprinting, and why?
- Fraud and security teams use it to spot account takeovers and bots.
- Advertisers and analytics companies use it to follow visitors across sessions when cookies are blocked.
- Websites use it to keep one account from being shared or duplicated.
Some uses protect you. Others track you. The technique is the same.
Is fingerprinting legal?
Rules vary by country. In the EU and UK, privacy law generally treats fingerprinting like other tracking that needs notice and, in many cases, consent. Elsewhere the rules differ. This article is general information, not legal advice.
How can you test your own fingerprint?
You can check what your browser reveals in a few minutes:
- Open the EFF’s Cover Your Tracks tool (the successor to Panopticlick, explained here) and run the test. It tells you whether your browser looks unique and which values stand out.
- Open a second test such as BrowserScan or CreepJS and compare. Different tools check different signals.
- Run the test again in a private window and again after clearing cookies. Note what does not change.
Your values stay the same across all three runs. That stability is what makes a fingerprint work.
Can you reduce your fingerprint?
There are two common approaches, and they work differently:
- Blend in. Use a very common setup, so many people share your values. Some privacy-focused browsers aim for this.
- Keep identities separate and consistent. Use a distinct, realistic identity for each purpose, so your accounts or sessions are not linked to each other. The values must agree with each other. A browser that claims one country and a different time zone, or one operating system and the fonts of another, stands out immediately.
The second approach is what multi-account tools, including VANE, are built around: each profile has its own isolated storage and its own consistent set of values, so one profile does not share a fingerprint with another.
Frequently asked questions
Does clearing cookies stop fingerprinting?
No. Fingerprinting does not rely on cookies, so clearing them has no effect on it.
Does private browsing stop fingerprinting?
Not by itself. Private mode keeps history and cookies off your device, but your browser still reports the same details to the sites you visit.
Does a VPN stop fingerprinting?
A VPN changes your IP address, not your browser’s details. Your fingerprint can stay the same behind a VPN.
Can a fingerprint change over time?
Yes. A browser update, a new font or a new screen can change it. Sites that track fingerprints usually match “close enough” and not only exact copies.
Is a unique fingerprint bad?
Being unique makes you easy to follow across sites. For privacy, blending in or keeping separate identities is generally preferable to being rare.
Key takeaways
- A fingerprint is built from many ordinary details, not from stored files.
- Clearing cookies and private browsing do not remove it.
- You can test yours in minutes with free tools.
- Consistency matters: values that contradict each other are a stronger signal than any single value.
Last updated: 2026-10-26. By the VANE Team.